Managed Keycloak features for production
Production-ready identity and access management, with the operational complexity handled for you.
Deploy is the easy part
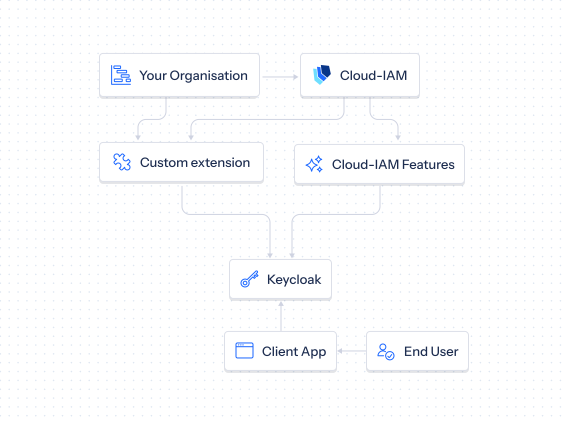
Running Keycloak in production is more than spinning up a container. Availability, upgrades, monitoring, backups become a full-time job, fast. Cloud-IAM covers the full lifecycle, so your team stays focused on what ships your product.
500+ customers trust us


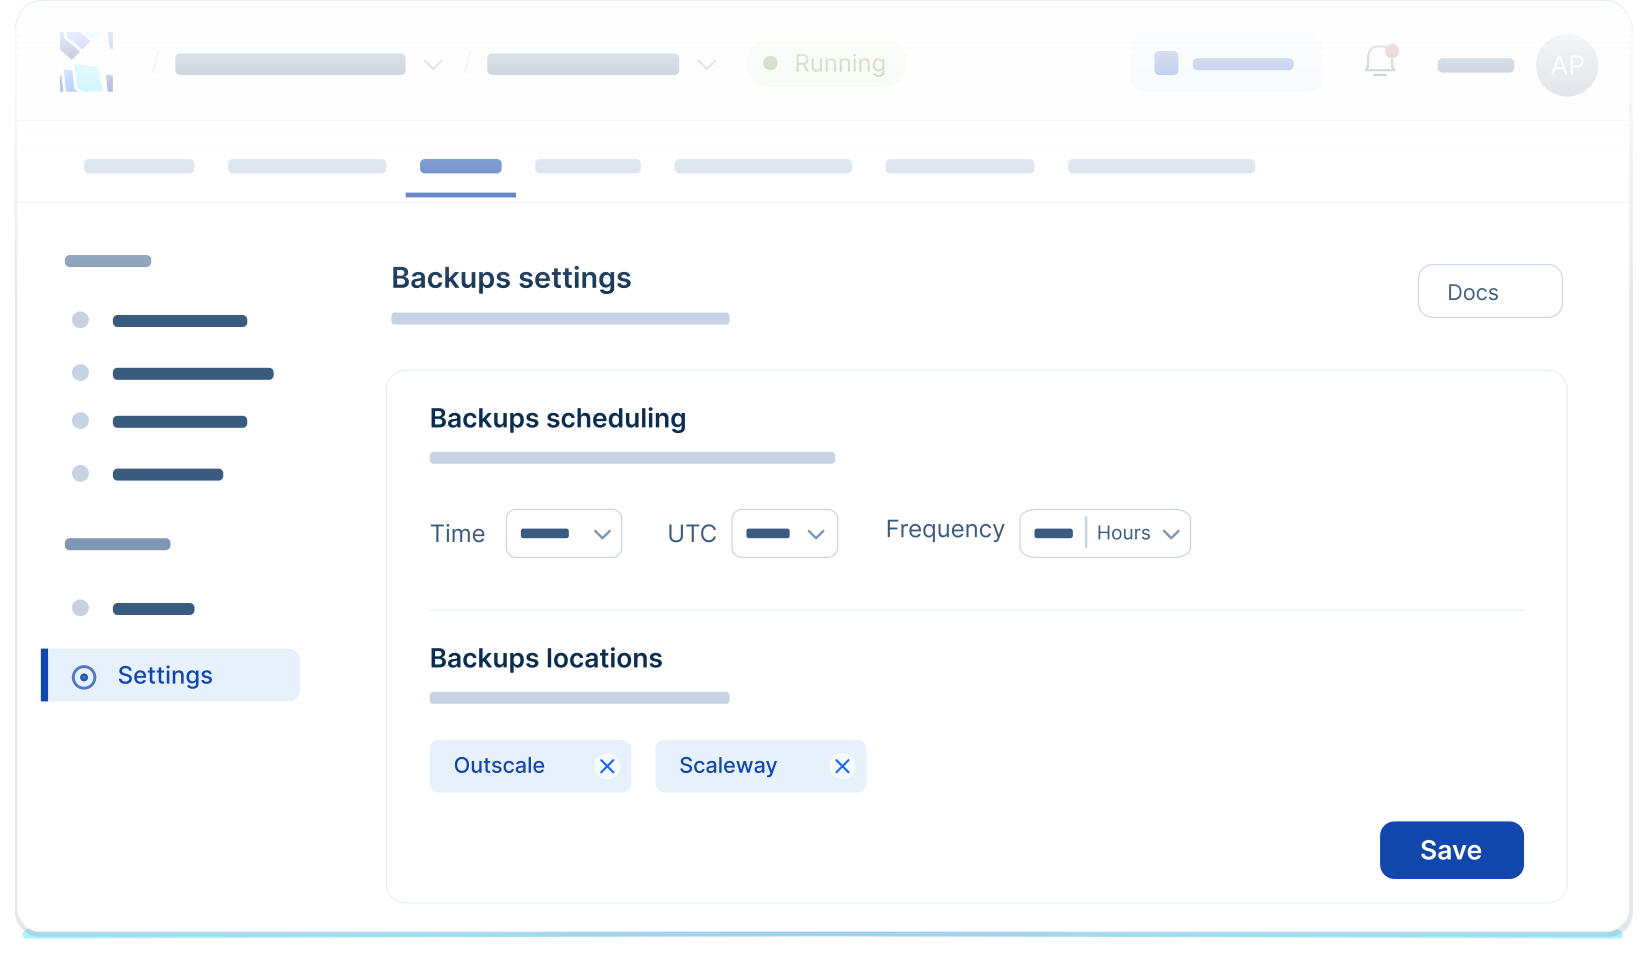
Backups & data ownership
Staying in control of your identity data means being able to back it up, export it, encrypt it and move it, on your terms, at any time.
Scheduling adapted to your operational needs, with snapshot and cold backup retention.
API access to manage, export and automate your backup workflows.
Complete exports including configuration, realms, users, groups and roles
Import and export support to retain full cryptographic control over your data
Deploy and store data where your compliance requirements demand
Import your own data and retain the ability to move or restore your environments at any time
Operate and maintain your IAM platform over time, without operational overload
Keycloak doesn't stop at deployment. Upgrades, incidents, 3am pages. We take that off your plate, so your team stays focused on shipping
Tested upgrade paths with automatic backup and one click rollback. No more upgrade Fridays.
Restarts, configuration changes and instance-level controls with clear visibility
Automate lifecycle operations and integrate them into your existing tooling and pipelines
Access to a dedicated team when operational incidents require expert intervention
One library for every Keycloak extension you run
Import your own custom extensions into your organization library, pick from the ones Cloud-IAM ships, and install them across your deployments in a few clicks. Each extension shows its Keycloak compatibility, its release history and where it is installed.
Upload your custom extensions once at the organization level. They become available to install on any deployment, without re-uploading.
Use our vetted extensions for passwordless login, OTP email and SMS, identity provider setup, webhooks and more. Some included, some available on purchase.
Pin a release, upgrade, or roll back. Full release history per extension
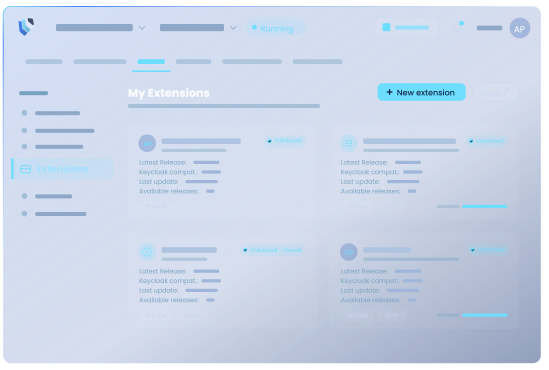
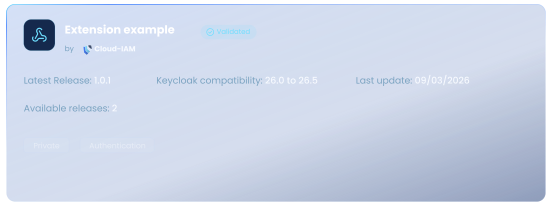
Every extension lists its supported Keycloak versions and release notes. You see compatibility before you install, not after a failed upgrade.
All for predictable pricing. No surprise
No hidden fees. Transparent pricing you can count on. Use our intuitive cost calculator to plan ahead with confidence.
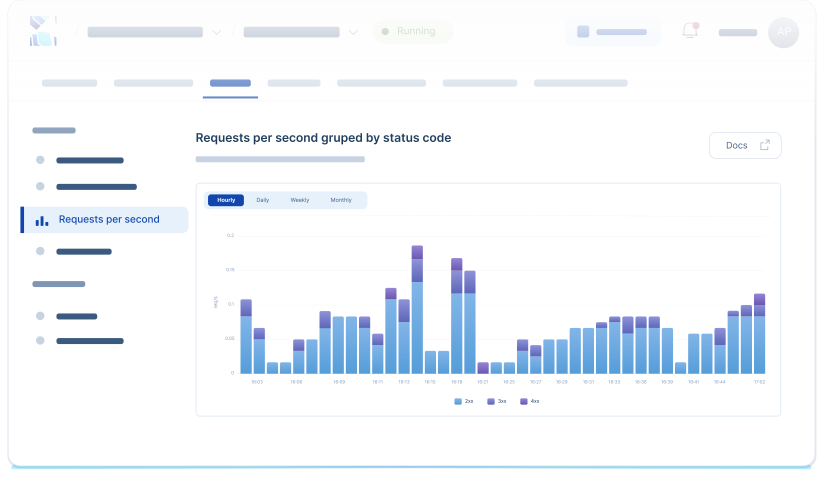
Full visibility into your Keycloak environments
Understanding what is happening inside your IAM platform is a prerequisite for operating it reliably. From authentication activity to infrastructure metrics, every tool below gives you the transparency needed to act before issues become incidents.
Full record of administrative actions across your Keycloak environments
Authentication events, login attempts, token issuance and errors
Inbound request history for forensic analysis and compliance reporting
Infrastructure-level visibility for debugging and incident investigation
QPS, token volume, active users, login rates and growth trends across your deployments
Monitor and manage blocked addresses directly from the platform
Export logs and metrics to your existing observability stack
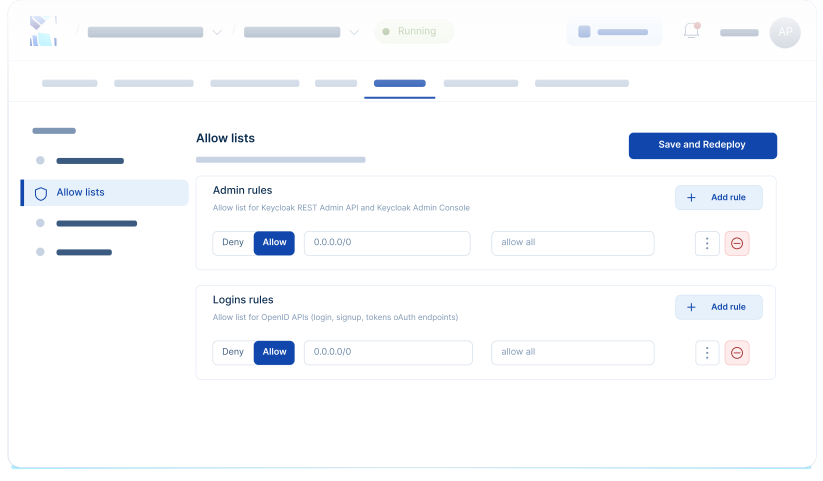
Keycloak provides strong authentication foundations
Keycloak provides strong authentication foundations. The controls below extend that baseline at the infrastructure and configuration level, giving your team the tools to harden any deployment for production.
Configure and inject environment-level variables securely into your Keycloak instances
Restrict access to your Keycloak environments to trusted IP ranges
Enable or disable Keycloak experimental and preview features directly from the Cloud-IAM console
Assign and manage several domains across your deployments
Additional controls to secure access to the Keycloak administration console
Manage configuration options beyond what is exposed natively in the Keycloak admin UI
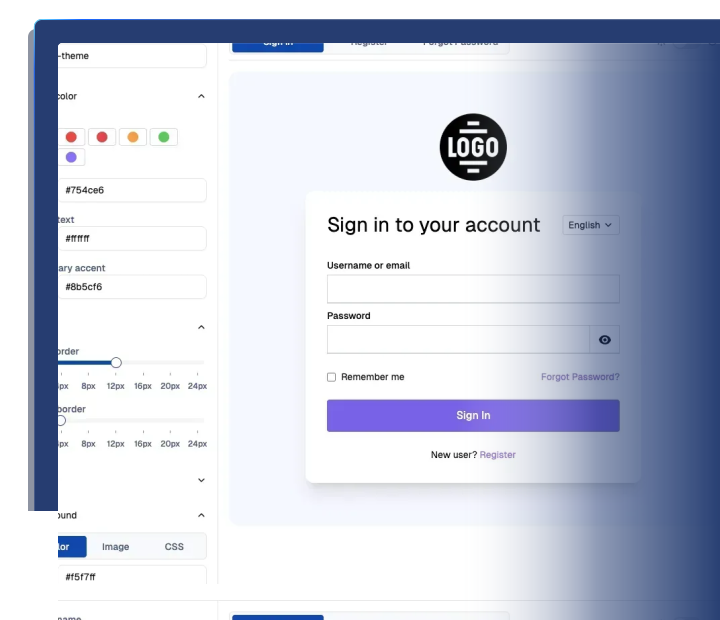
Brand and extend Keycloak to match your product and business logic
Your identity layer is part of your product experience. Customize Keycloak's look, feel and behavior, without recompilation, without redeployment, without friction.
Customize your authentication flow
Design and configure login pages visually, without touching templates or stylesheets
Create, maintain and switch between themes across your environments
Apply changes without restarting or redeploying your Keycloak instance
Custom domains
Serve your Keycloak instance under your own domain, with multi-domain support.
Instant visibility into the health of your Keycloak deployment
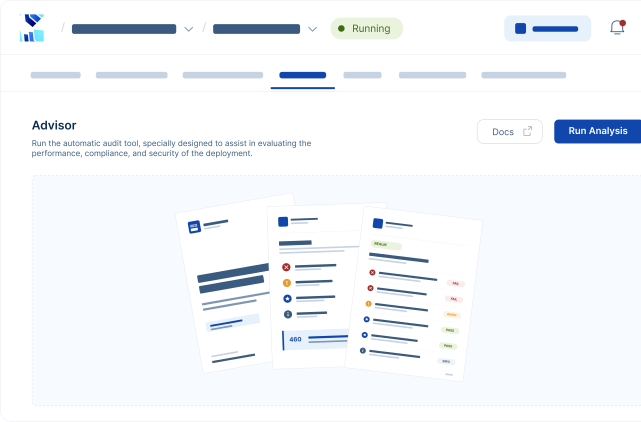
Misconfigurations accumulate over time, and most are only discovered when something goes wrong. Run an automated scan of your Keycloak environment and get a complete report in minutes, with prioritized findings and actionable guidance to fix them.
A full scan of your deployment configuration triggered on demand
A structured analysis of your settings, policies and configurations against best practices
Findings ranked by severity level, so your team knows what to fix first
Each finding comes with clear guidance to resolve the issue directly in your environment